From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths
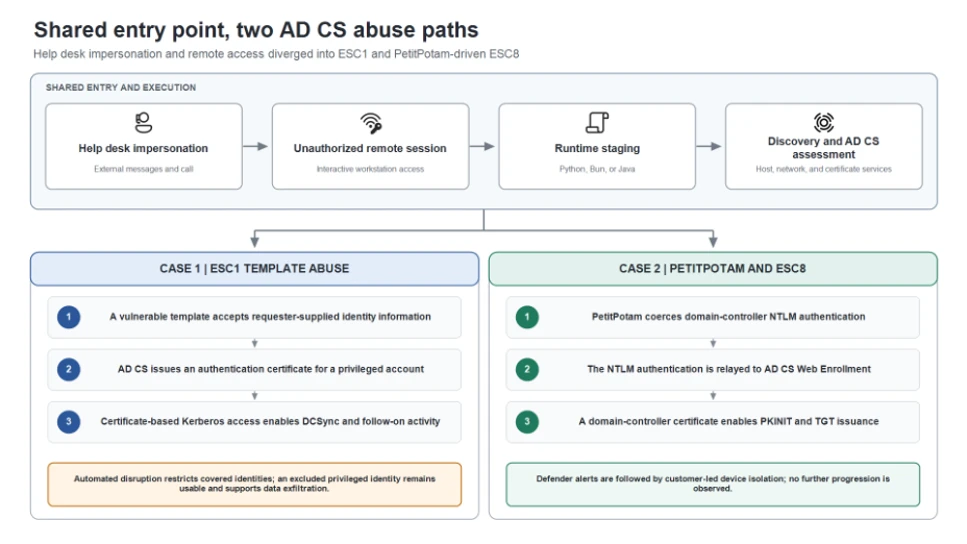
Teams support impersonation led to remote access, malicious runtime execution, and Certificate Services abuse through authentication relay and Kerberos. The post From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths appeared first on Microsoft Security Blog .
Published by Microsoft Threat IntelligenceOpen original story
Magazine Core indexes and summarizes the source. The complete article remains with its original publisher.